Cloud services have become part of doing business for most defense contractors. But when a cloud service will process, store, or transmit Controlled Unclassified Information (CUI), the question is no longer just whether the service meets your organization’s business needs. You also have to understand whether it can meet the security and compliance requirements that come with handling CUI.
That brings us to FedRAMP 20x.
The Federal Risk and Authorization Management Program (FedRAMP) is changing how cloud services obtain and describe federal certification. For organizations in the Defense Industrial Base (DIB), the terminology may be changing, but the underlying question remains the same: what does the cloud provider's compliance claim actually mean for the service you intend to use?
If the service will process, store, or transmit CUI, you need to understand what was certified, which certification class applies, whether the certification covers the specific service you intend to use, and whether the provider actually holds FedRAMP certification or is relying on a FedRAMP Moderate equivalency claim.
A vendor saying it is "FedRAMP certified" or "FedRAMP 20x certified" may sound reassuring,. but the claim by itself doesn’t tell you enough to make a decision.
If the service will process, store, or transmit CUI, you need to look a little deeper. What exactly was certified? Which certification class applies? Does the certification cover the specific service and environment you plan to use? And is the provider actually FedRAMP certified, or are they making a FedRAMP equivalency claim?
FedRAMP 20x: Why "Certified" Is Not Enough for Defense Contractors
Defense contractors have become familiar with terms like FedRAMP Moderate when evaluating cloud services. FedRAMP 20x introduces new terminology and certification classes, but the basic due diligence hasn’t changed. You need to understand exactly what a provider’s certification covers.
A cloud provider may accurately say that it has a FedRAMP certified offering. That doesn’t necessarily mean that the service, environment, or configuration your organization plans to use is covered by that certification.
If a cloud service may handle CUI, I would start with three questions:
| What certification class applies? Identify the FedRAMP class associated with the service. | |
| What specific Cloud Service Offering (CSO) is covered? Make sure the certification applies to the product and environment you actually plan to use. | |
| Is it certification or equivalency? Determine whether the provider holds FedRAMP certification for the offering or is making a FedRAMP Moderate equivalency claim. |
Those answers tell you much more than a FedRAMP logo or a general compliance statement on a vendor’s website. With those distinctions in mind, it’s worth looking at what FedRAMP 20x actually changes.
What Is FedRAMP 20x?
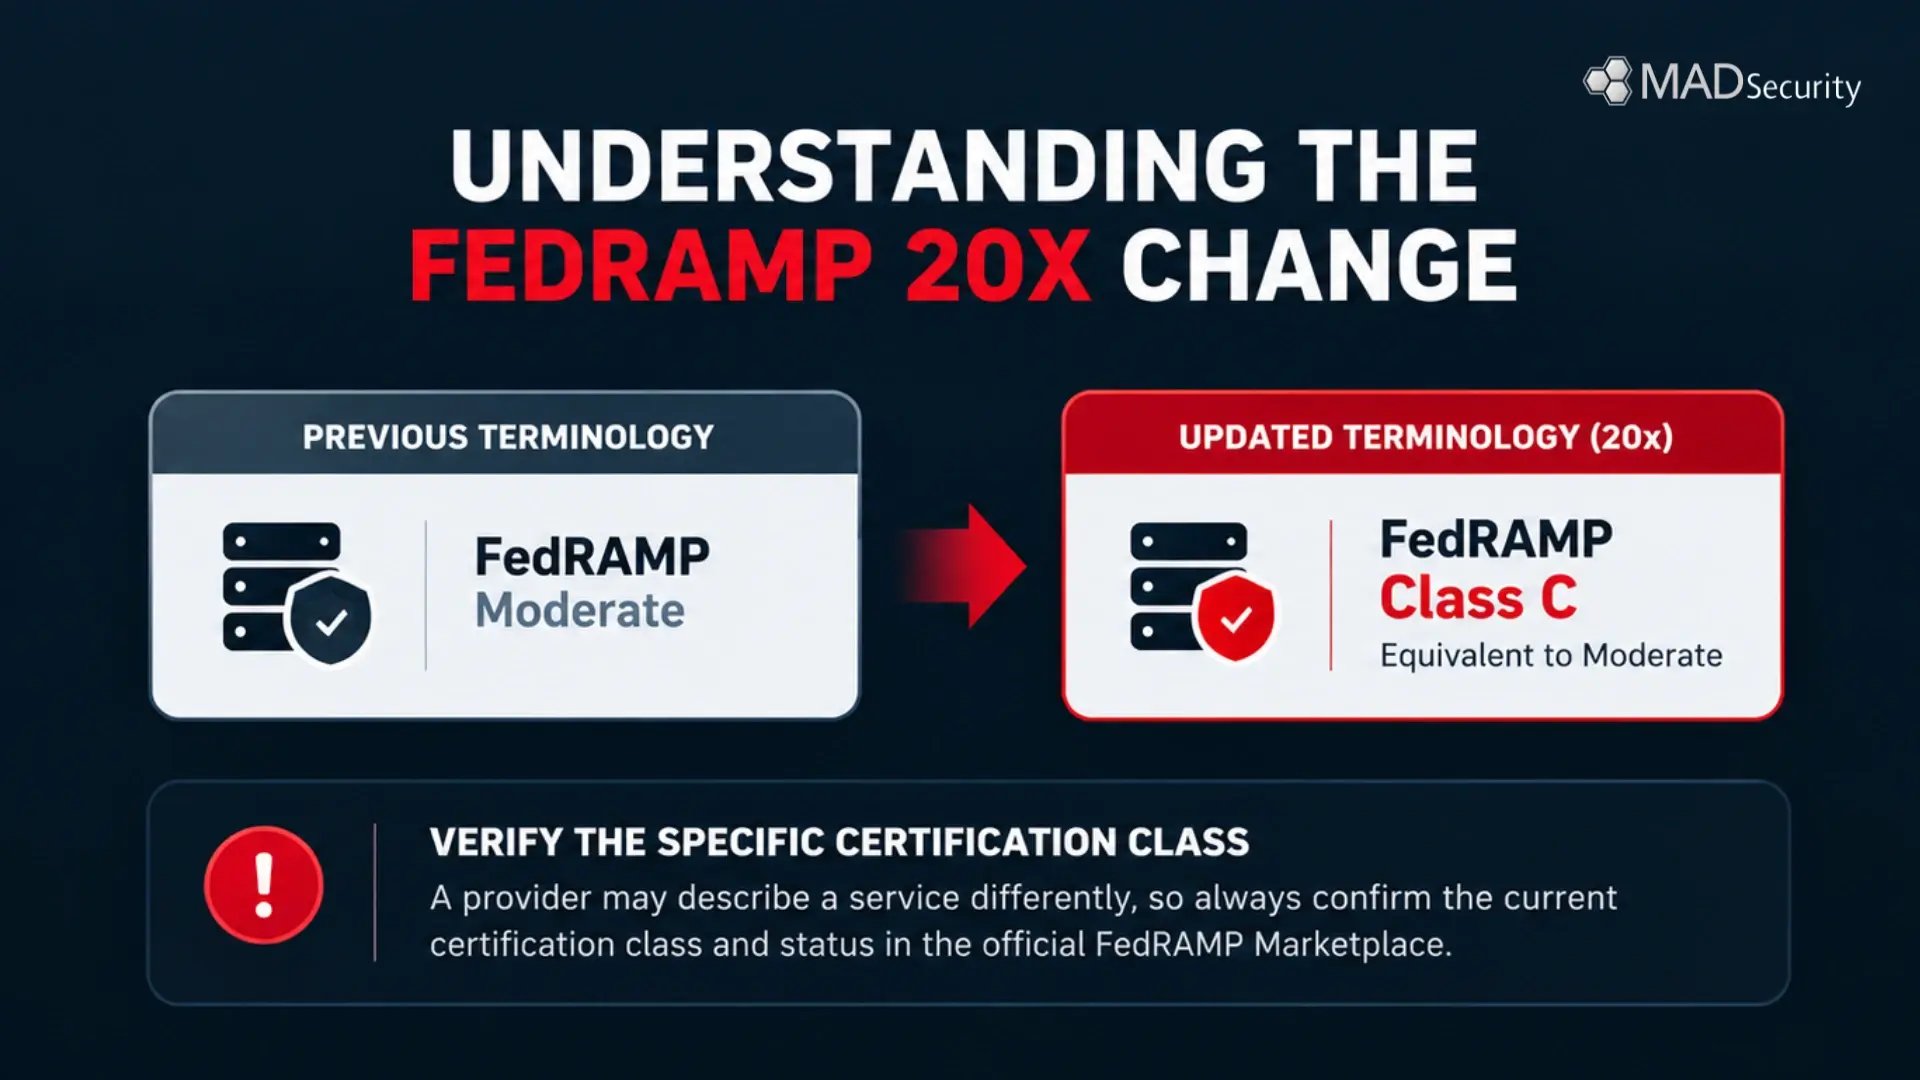
The distinction is important because "FedRAMP 20x certified" by itself doesn’t tell you which class applies or whether the certification is appropriate for how you intend to use the service.
For a defense contractor evaluating a cloud service, the practical questions are still fairly straightforward. Which class applies? What is the current certification status? And does that certification covers the specific service and environment you intend to use?
Those questions become particularly important when that service enters the CUI environment.
Why FedRAMP 20x Matters for Cloud Services Handling CUI
When a cloud service will store, process, or transmit CUI, vendor due diligence becomes more than a normal technology purchasing decision.
 Defense Federal Acquisition Regulation Supplement (DFARS) requirements address the use of external cloud service providers for covered defense information. When those requirements apply, a contractor using an external cloud provider to store, process, or transmit that information needs to ensure the service meets the applicable cloud security requirements, including FedRAMP Moderate equivalency.
This fits with the broader cybersecurity requirements defense contractors are already managing under National Institute of Standards and Technology Special Publication 800-171 (NIST SP 800-171) and the Cybersecurity Maturity Model Certification (CMMC) program. The practical point is simple: don’t evaluate the cloud company only. Evaluate the exact cloud service you intend to use.
A large provider may offer dozens of products, deployment options, and environments. A FedRAMP certification associated with one service shouldn’t automatically be assumed to cover everything that provider sells.
Before approving a cloud service for use with CUI, I would want to answer a few basic questions:
| Which specific offering will process, store, or transmit the CUI? | |
| What FedRAMP class and certification status apply to that offering? | |
| Is the environment or deployment model you intend to use within the scope of this certification? | |
| Does the provider hold an actual certification for that offering, or is it relying on FedRAMP Moderate equivalency? | |
| What documentation supports the provider's claim? |
Using a third-party cloud service doesn’t transfer the contractor’s responsibility for protecting CUI. You still need to understand where the information is going, how it will be protected, and what evidence supports the provider’s claims.
That last question is particularly important because FedRAMP certification and FedRAMP Moderate equivalency are related, but they aren’t the same thing.
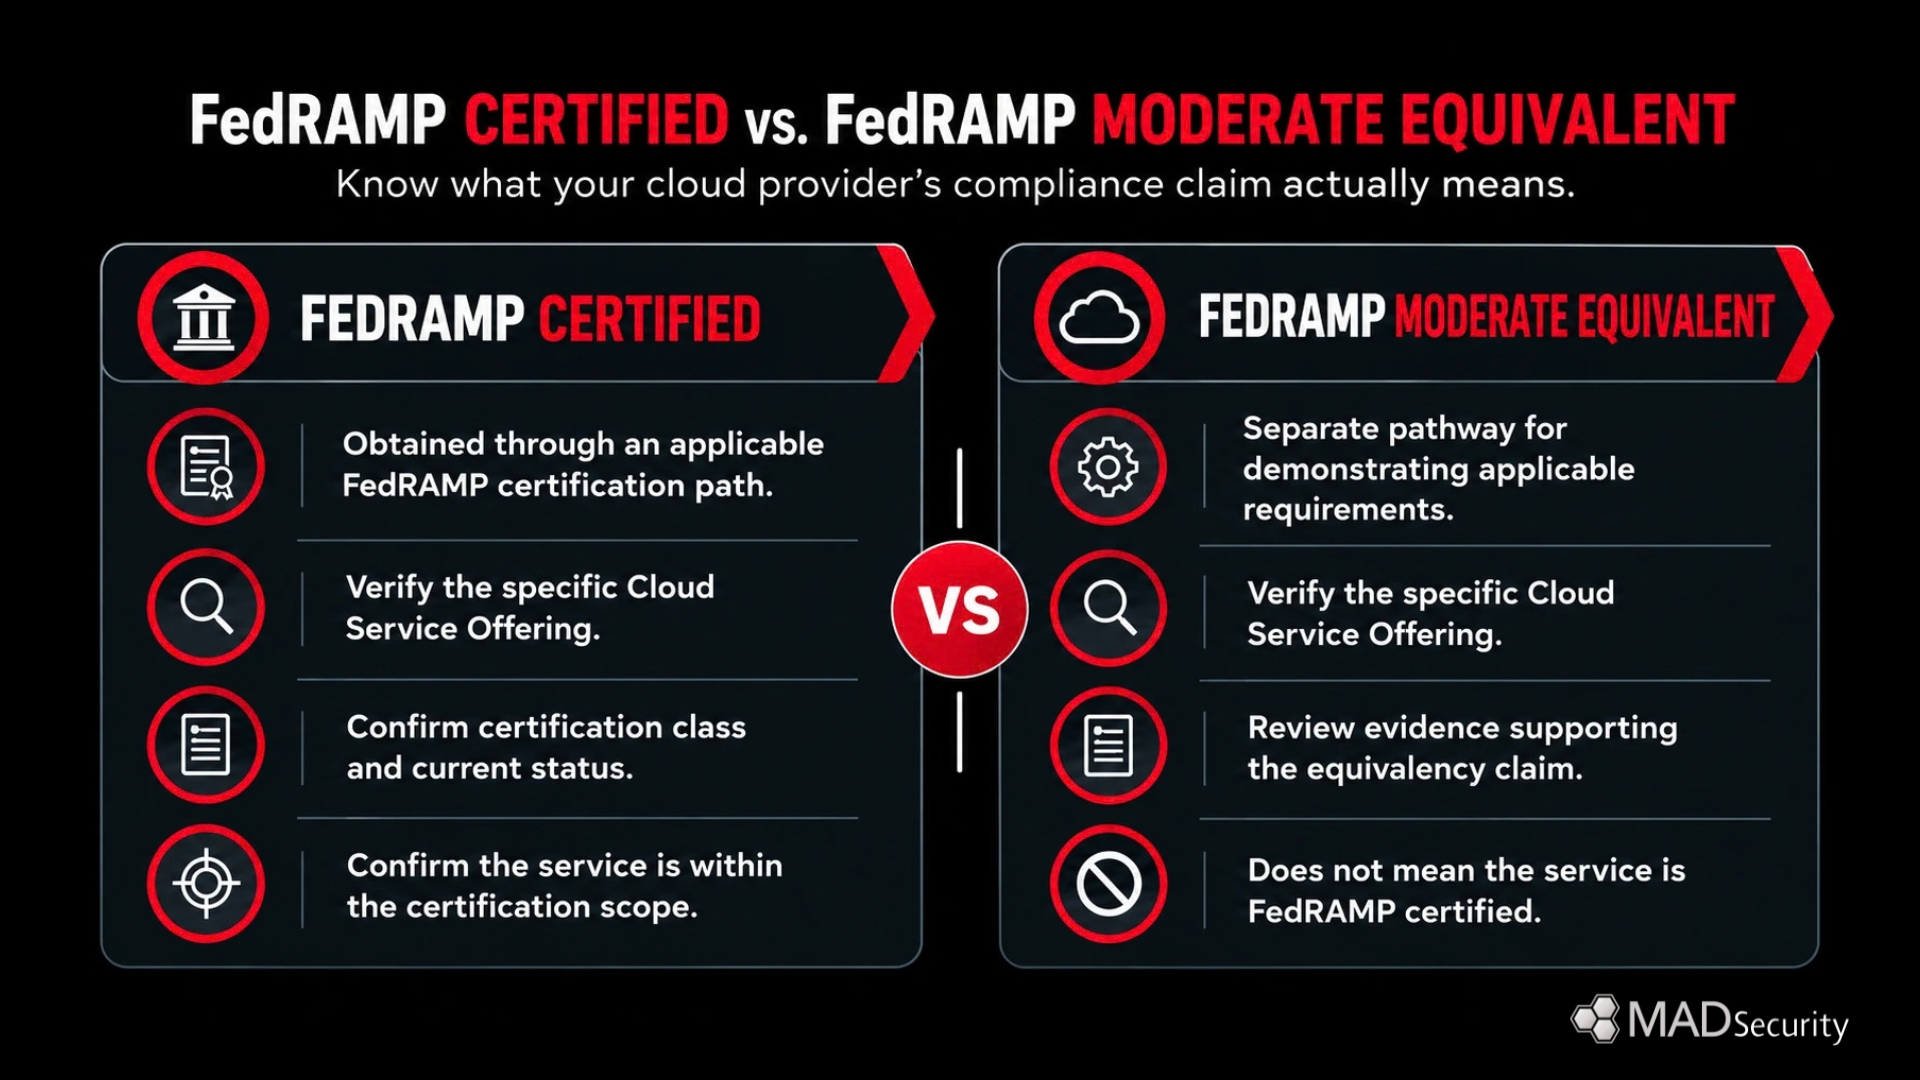
FedRAMP Certification vs. FedRAMP Moderate Equivalency
The terms sound similar enough that they are sometimes used loosely in vendor conversations, but FedRAMP certification and FedRAMP Moderate equivalency ot interchangeable.
FedRAMP Certification
A FedRAMP-certified offering has obtained certification through an applicable FedRAMP certification process.
When a provider makes that claim, I would still want to understand exactly what the certification covers. Under the current FedRAMP structure, that means looking at the certification type, class, status, and specific Cloud Service Offering covered by the certification.
The practical question is whether the certification applies to the same service and environment your organization intends to use for processing, storing, or transmitting CUI. A FedRAMP certification somewhere in the provider’s portfolio doesn’t necessarily answer that question.
FedRAMP Moderate Equivalency
FedRAMP Moderate equivalency is a different path.
DFARS allows an external cloud provider handling covered defense information to meet security requirements equivalent to the FedRAMP Moderate baseline. A provider relying on equivalency is asserting that its service meets those requirements without claiming that the offering has obtained FedRAMP certification.
The difference is important when you’re evaluating the provider’s claim. If a vendor says it’s service is "FedRAMP equivalent," that shouldn’t be interpreted to mean "FedRAMP certified." Instead, I would want to understand exactly what the provider is claiming and review the evidence supporting that position.
Whether the provider is relying on certification or equivalency, I would come back to the same basic questions:
| What specific offering does the claim cover? | |
| What certification or equivalency pathway applies? | |
| What is it’s current status? | |
| What documentation supports the claim? |
The goal isn’t to collect another compliance badge for your vendor file. The goal is to understand whether the cloud service you are relying on is appropriate for the information you intend to put there.
Three Questions to Ask a Cloud Provider Before It Handles CUI
 |
Which specific CSO will handle our CUI? Identify the specific product, service, deployment model, and environment that will process, store or transmit the CUI. Then make sure the FedRAMP claim applies to that offering. Don’t assume a company-wide compliance statement covers every service the provider offers. |
 |
What FedRAMP status applies? Determine whether the offering holds actual FedRAMP certification or whether the provider is relying on FedRAMP Moderate equivalency. If the offering is FedRAMP 20x certified, verify the applicable class and current status rather than relying on the general "FedRAMP certified" statement. |
 |
What evidence supports the claim? Ask the provider to for documentation supporting its position. More importantly, make sure the documentation applies to the specific service and environment your organization intends to use. These questions get you past the terminology and back to what matters: understanding the cloud specific cloud service that will handle your CUI, and having evidence to support he decision to use it. From there, this kind of verification should become part of your normal vendor-management process.
|
Build FedRAMP Verification into Your Cloud Vendor Reviews
It’s much easier to address these questions before a cloud service is purchased and deployed than to discover later that the service doesn’t meet the requirements for handling CUI.
For services already in use, I would start by identifying which ones are part of the CUI environment and work through the same questions. Going forward, that review can become part of the normal procurement and vendor-management process.
For each relevant service: