For Department of Defense (DoD) contractors, identifying Controlled Unclassified Information (CUI) is an important part of protecting sensitive government information. But knowing that information is CUI is only the beginning. You also need to understand what type of CUI you handle, and which safeguarding and dissemination requirements apply to it.
That starts with understanding the difference between CUI Basic and CUI Specified. CUI Basic follows the standard safeguarding and dissemination requirements established under the CUI Program. CUI Specified is different because the law, regulation, or government-wide policy governing that information establishes specific requirements that may affect how it must be protected or shared.
For DoD contractors and subcontractors, that distinction has practical consequences. It can influence your policies and procedures, security controls, employee responsibilities, and how CUI is shared with authorized third parties.
So, identifying information as CUI should lead to another question: What requirements follow that information? Answering it requires knowing the applicable CUI category, whether the information is CUI Basic or CUI Specified, and the safeguarding and dissemination requirements your organization needs to address.
What Is Controlled Unclassified Information (CUI)?
 Before you can determine whether information is CUI Basic or CUI Specified, it helps to understand what qualifies as Controlled Unclassified Information (CUI) in the first place. CUI is information that requires safeguarding or dissemination controls under applicable laws, regulations, and government-wide policies but is not classified information.
That distinction is important. Although CUI does not carry a classified designation, it still requires appropriate protection against unauthorized access, disclosure, and sharing.
For DoD contractors and subcontractors, CUI can move through many parts of the organization. Employees may access it while performing contract work, systems and applications may process or store it, and authorized information may need to be shared with subcontractors, suppliers, or other external recipients. Understanding where CUI resides and how it moves is an important part of protecting it.
Identifying information as CUI does not necessarily tell you everything you need to know about handling it. You also need to identify the applicable CUI category because different categories may be governed by different safeguarding and dissemination requirements.
This is where understanding CUI Basic vs. CUI Specified becomes especially important. Knowing the category helps your organization determine which requirements apply, and how those requirements should be reflected in your policies, procedures, security controls, and information-sharing practices.
With that foundation in place, the next step is understanding what makes information CUI Basic.
What Is CUI Basic?
Once you know which CUI categories your organization handles, the next step is understanding the requirements that follow that information. For many contractors, that starts with CUI Basic.
CUI Basic applies when the law, regulation, or government-wide policy governing the information does not establish specific safeguarding or dissemination controls. Instead, the information is handled according to the standard requirements established by the CUI Program. These requirements are intended to protect CUI from unauthorized access or disclosure while establishing appropriate controls for how the information is shared.
The word “Basic” can be misleading. It does not mean the information requires minimal protection, presents little risk, or can be handled informally. Contractors still need to understand where CUI Basic exists within their environment and make sure applicable requirements are reflected in everyday handling practices.
|
Where CUI is stored and processed: Know which systems, applications, and environments contain the information |
|
|
Who can access it: Limit access to authorized individuals based on applicable requirements. |
|
|
How it is transmitted or shared: Understand how CUI moves internally and when it is provided to authorized external recipients. |
|
|
How it is protected: Make sure policies, procedures, and security controls support applicable CUI safeguarding requirements and CUI dissemination requirements. |
The practical takeaway is simple: knowing that you handle CUI is not enough. You need to understand the categories you handle, and the requirements attached to them. That becomes even more important when a governing authority establishes specific controls, which brings us to CUI Specified.
What Is CUI Specified?
CUI Basic gives contractors a standard foundation for protecting and sharing information. CUI Specified requires an additional step: understanding the authority that governs the CUI category.
CUI Specified applies when a law, regulation, or government-wide policy establishes specific safeguarding or dissemination controls for that information. Those requirements may be additional to or different from the standard requirements that apply to CUI Basic. This is why identifying the governing authority is important. It helps contractors understand what is actually required rather than relying on a general approach to CUI protection.
Depending on the category, those requirements can influence how an organization protects and manages the information, including access, handling procedures, security controls, and how CUI is shared with authorized recipients. Specific dissemination requirements may also affect who can receive the information or the conditions under which it can be shared.
It is also important not to interpret “Specified” as simply meaning “more sensitive.” The distinction is based on whether the governing law, regulation, or government-wide policy establishes specific controls for that CUI category. In practice, contractors need to understand the requirements attached to the information, not make assumptions based on the label alone.
For organizations handling CUI Specified, that means documenting the applicable category, identifying its governing authority, and determining which safeguarding and dissemination requirements apply. Those requirements should then be reflected in relevant policies, procedures, technical protections, and information sharing practices.
Ultimately, identifying information as CUI only gets you so far. Understanding whether it is CUI Basic or CUI Specified provides the context needed to determine how that information should be handled, which makes a direct comparison between the two especially useful.
CUI Basic vs. CUI Specified: What Is the Difference?
Now that we have looked at each type individually, the difference between CUI Basic and CUI Specified comes down to where the applicable requirements originate. CUI Basic follows the standard requirements of the CUI Program, while CUI Specified is subject to specific controls established by the law, regulation, or government-wide policy governing that category.
For contractors, this distinction matters because it can affect both safeguarding and dissemination. With CUI Basic, organizations follow the standard requirements for protecting and sharing information. With CUI Specified, contractors need to identify the governing authority and determine whether specific requirements apply to how the information is protected, handled, or shared.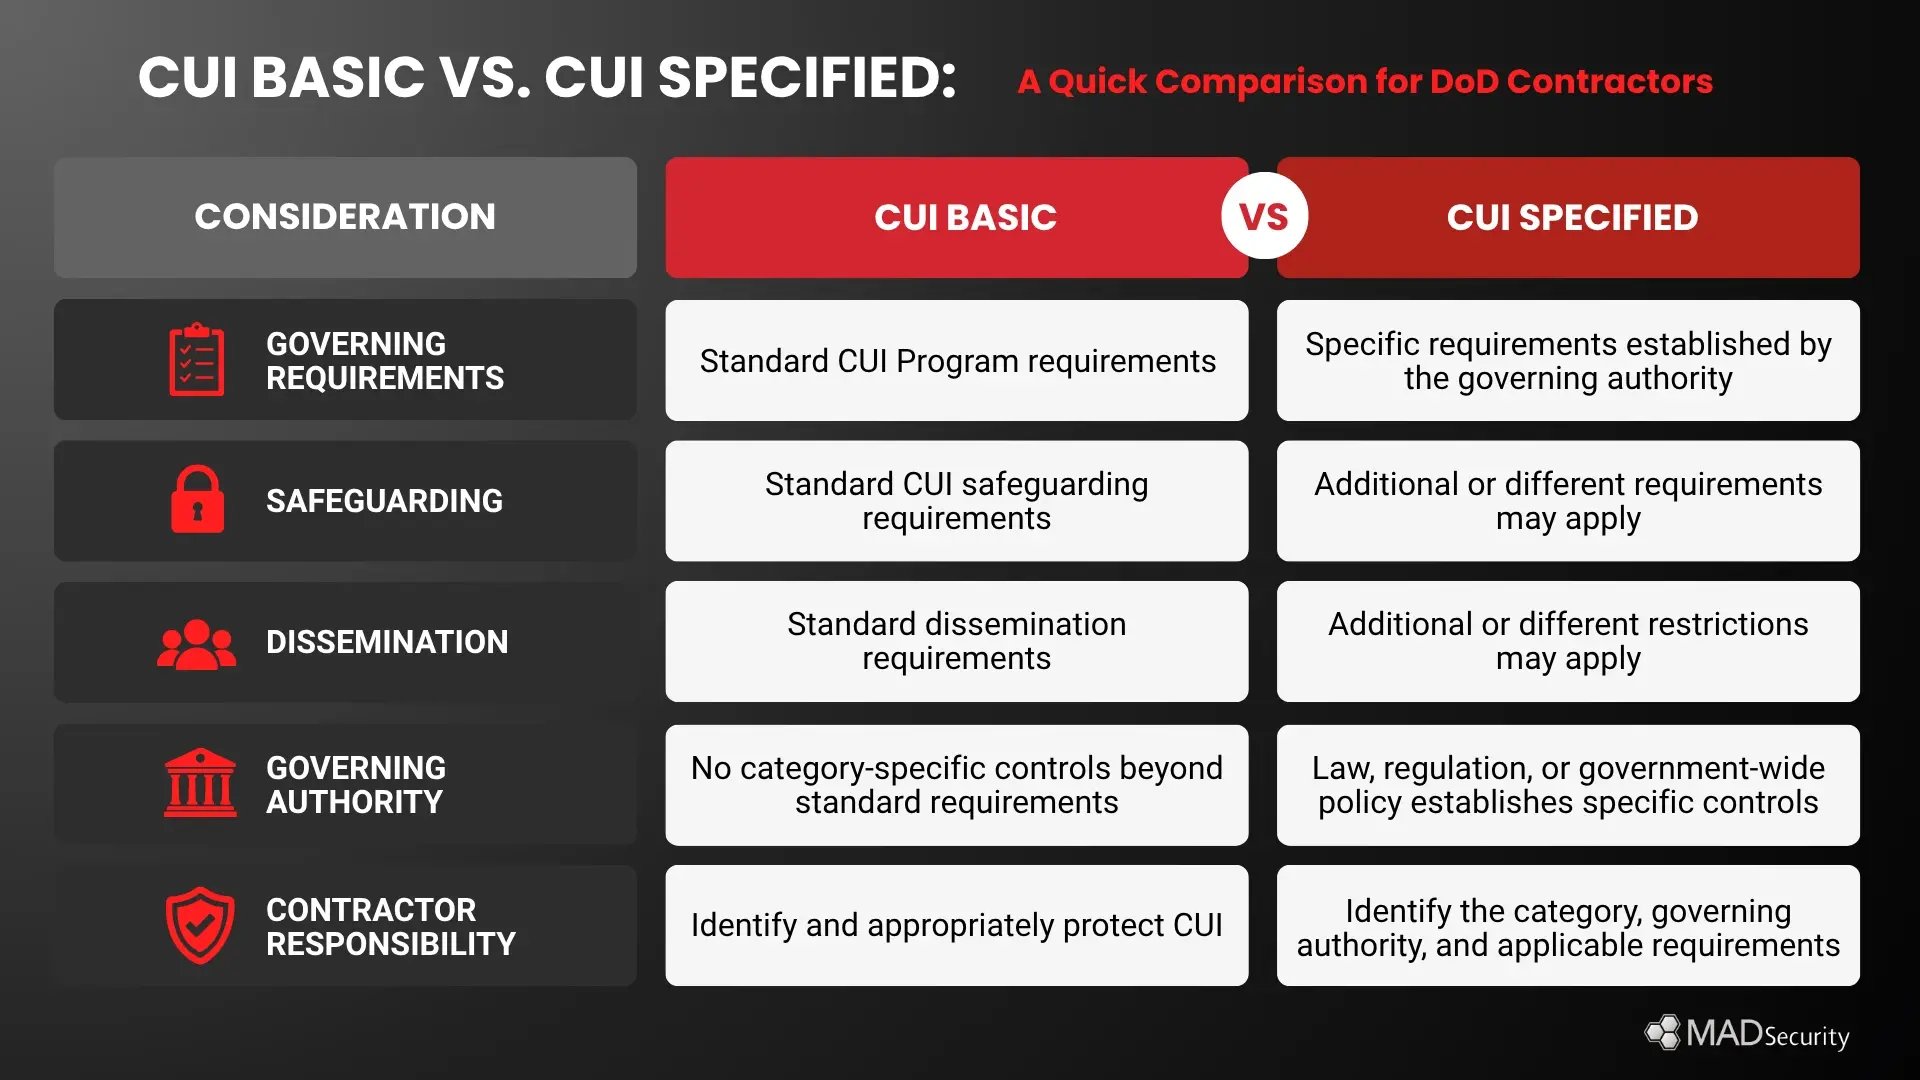
The distinction is not simply about whether one type of CUI is considered more sensitive than another. It is about understanding which requirements govern the information and making sure those requirements are reflected in how your organization handles it.
A practical way to approach CUI Basic vs. CUI Specified is to answer three questions:
| What CUI does your organization handle? | |
| Which CUI categories apply? | |
| What safeguarding and dissemination requirements apply to those categories? |
Why CUI Basic vs. CUI Specified Matters for
DoD Contractors
Knowing whether you handle CUI Basic or CUI Specified is more than a classification exercise. For DoD contractors, correctly identifying the information and its applicable requirements helps shape how CUI is protected across people, processes, and technology.
When organizations treat all CUI the same, gaps can develop between what their policies say and how information is handled.
Those gaps can affect several areas of a contractor’s CUI program:
 |
Policies and procedures Documentation should reflect the safeguarding and dissemination requirements that apply to the CUI being handled.
|
 |
Access and handling Personnel should understand who is authorized to access CUI and how it must be protected throughout their work.
|
 |
Training and awareness Employees need practical guidance for recognizing, handling, and appropriately sharing the CUI they encounter.
|
 |
Security controls Technical and administrative protections should support the applicable CUI safeguarding requirements.
|
 |
Third-party sharing Contractors should understand applicable dissemination requirements before CUI is shared with subcontractors, suppliers, or other authorized recipients.
|
These considerations are also relevant when organizations address CMMC Level 2 and NIST SP 800-171 requirements for protecting CUI in applicable nonfederal systems and organizations. However, contractors should not assume that implementing one cybersecurity framework automatically addresses every requirement associated with every CUI category. CUI Specified may require organizations to consider requirements established by its governing authority as well.
 The goal is to make sure the right protections follow the information wherever it goes. That requires knowing which CUI categories you handle, understanding the requirements that apply, and making sure those requirements are reflected in day-to-day practices. From there, contractors can take a closer look at how individual CUI categories shape specific safeguarding and dissemination requirements.
How CUI Categories Determine Safeguarding and Dissemination Requirements
Once you understand which CUI categories your organization handles, the next step is connecting those categories to the requirements that govern the information. This is where categorization becomes practical. It helps determine how CUI should be protected, handled, and shared throughout its lifecycle.
Start by determining whether the applicable category is CUI Basic or CUI Specified. For CUI Basic, the standard CUI Program requirements apply. For CUI Specified, contractors also need to identify the governing law, regulation, or government-wide policy and understand the specific controls it establishes.
From there, it is important to look at both safeguarding and dissemination. Safeguarding focuses on protecting CUI from unauthorized access or disclosure, while dissemination addresses how and with whom that information may be shared.
Depending on the applicable requirements, these considerations can affect:
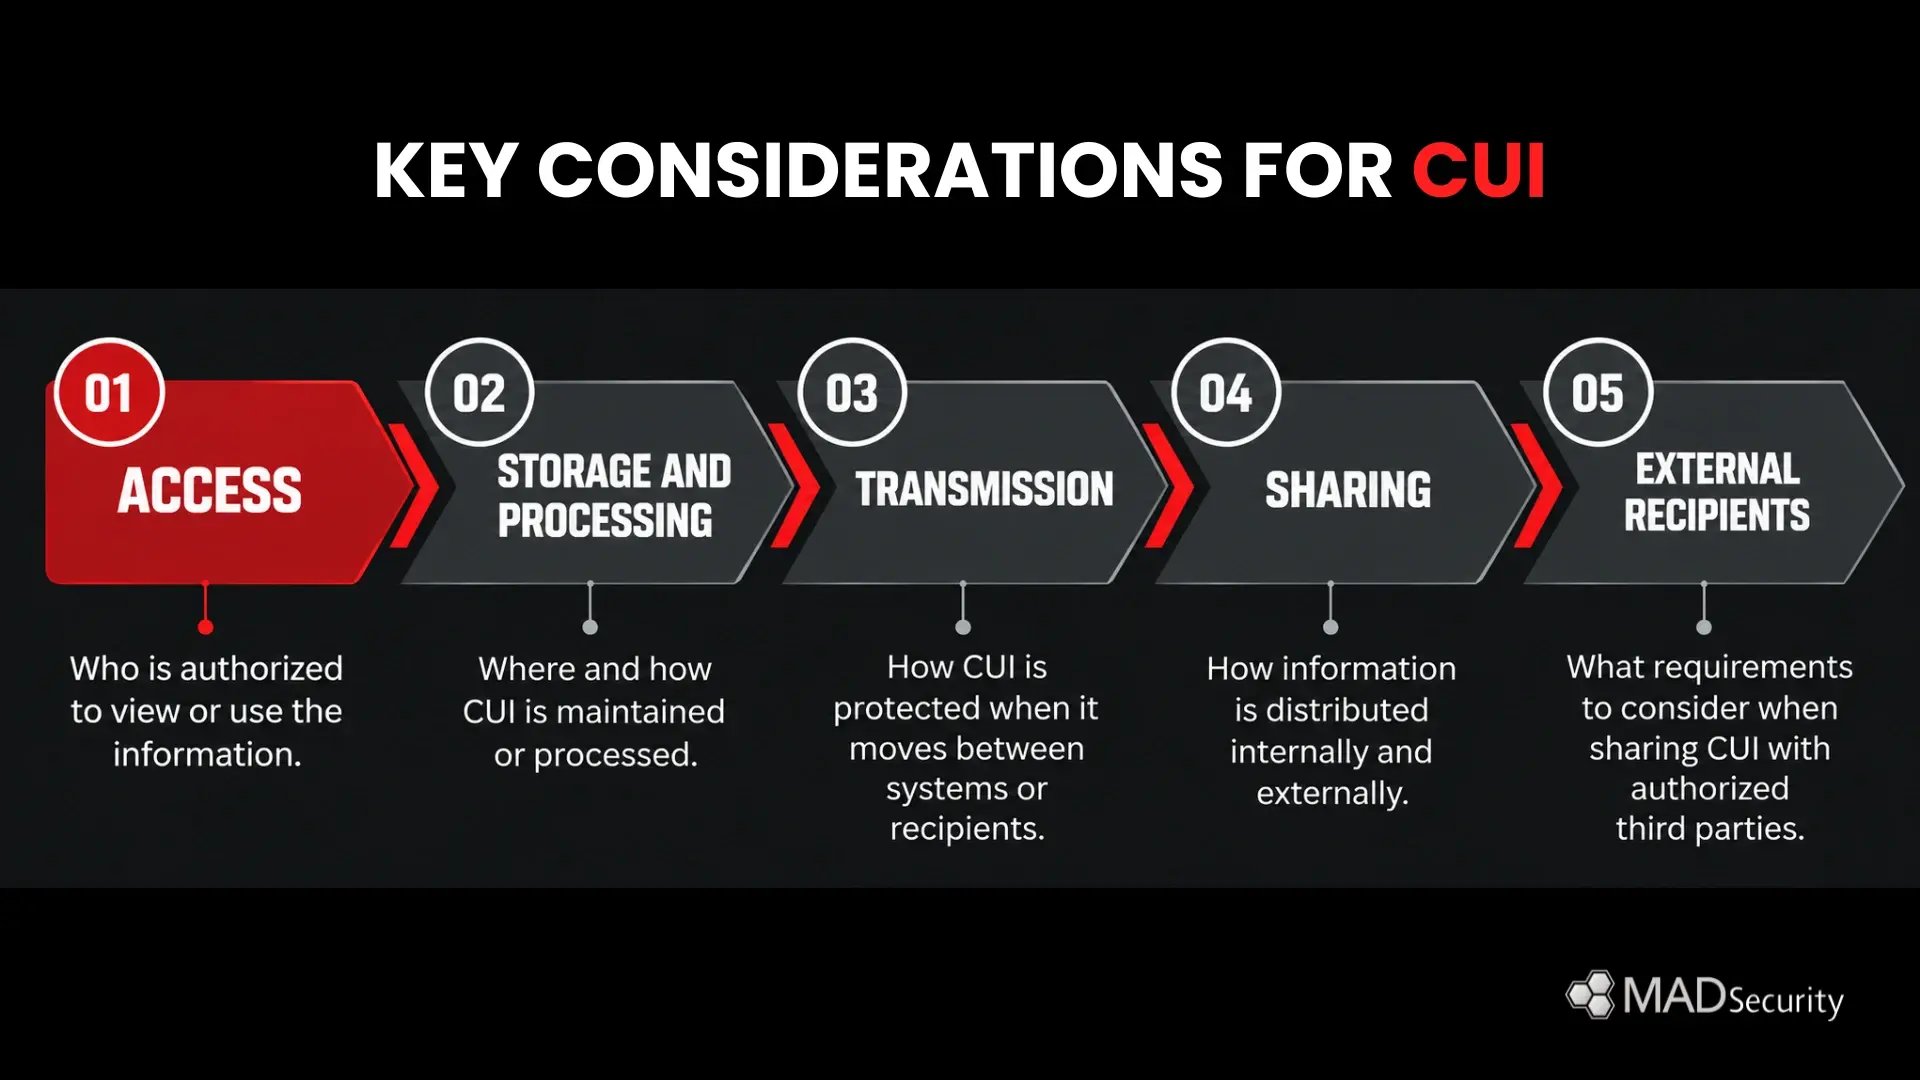
Contractors should compare these requirements with their existing policies, procedures, and technical and administrative controls. The goal is not simply to document a CUI category, but to make sure the appropriate protections follow the information wherever it is handled.
That understanding provides the foundation for a more structured review of your CUI environment, including where the information resides, how it moves, who has access to it, and whether current practices address the applicable requirements.
How to Review CUI Basic and CUI Specified in Your Organization
Understanding the requirements is important, but contractors also need a reliable way to apply them across the organization. A periodic CUI review can help you understand what information you handle, where it moves, and whether your current practices align with the requirements that apply.
A practical review should include the following:
|
Inventory the CUI you handle: Identify CUI your organization receives, creates, processes, stores, or transmits. Look beyond individual documents and consider the systems, applications, and business processes where that information exists. |
|
|
Map applicable CUI categories: Determine which categories apply and whether the information is CUI Basic or CUI Specified. |
|
| Identify governing authorities: For CUI Specified, document the applicable law, regulation, or government-wide policy that establishes specific controls. | |
| Document the requirements: Identify the safeguarding and dissemination requirements that apply to each relevant category. | |
| Compare requirements with current practices: Review policies, procedures, access controls, and other security measures to determine whether they support applicable requirements. | |